Last Update: 2026-8-26
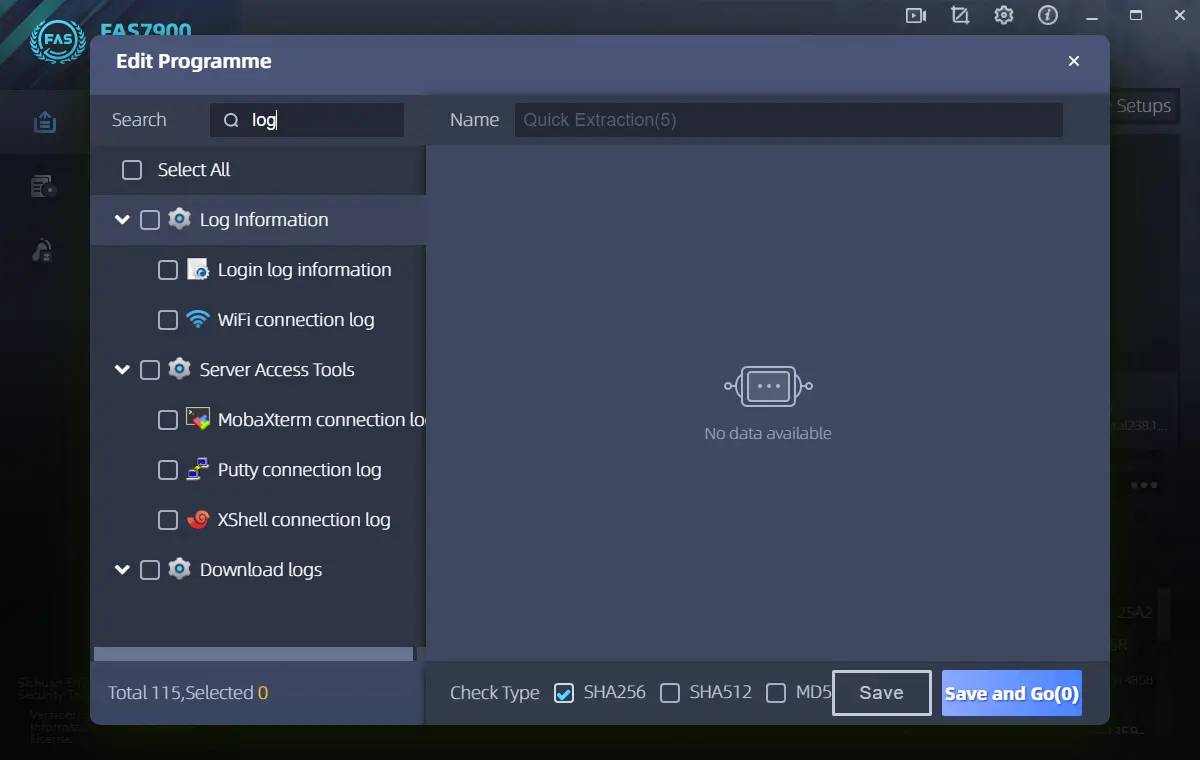
Forensic log analysis — sometimes called log forensics or logfile forensics — is the process investigators use to examine log files as digital evidence, reconstructing user behavior, system activity, and security incidents from the trail a system leaves behind. Unlike general IT log monitoring, forensic log analysis has to preserve evidentiary integrity at every step: investigators track activity, identify unauthorized access, and reconstruct timelines of events in a way that can hold up in an investigation or in court. Beyond just storing records, log files serve as computer log files evidence that supports digital investigations and contributes to data integrity. This guide walks through 10 forensic log analysis techniques and tools that digital forensics professionals rely on, from initial data collection through to final reporting.